Ventrix Research Team • Sep 23, 2026
The Board Seat Is Open. The Job Is Still Undefined.
A board search can begin before the company agrees on the job. A clear recruitment brief defines the contribution, evidence and terms candidates need to assess.
Aug 12, 2026
Ventrix Editorial Team
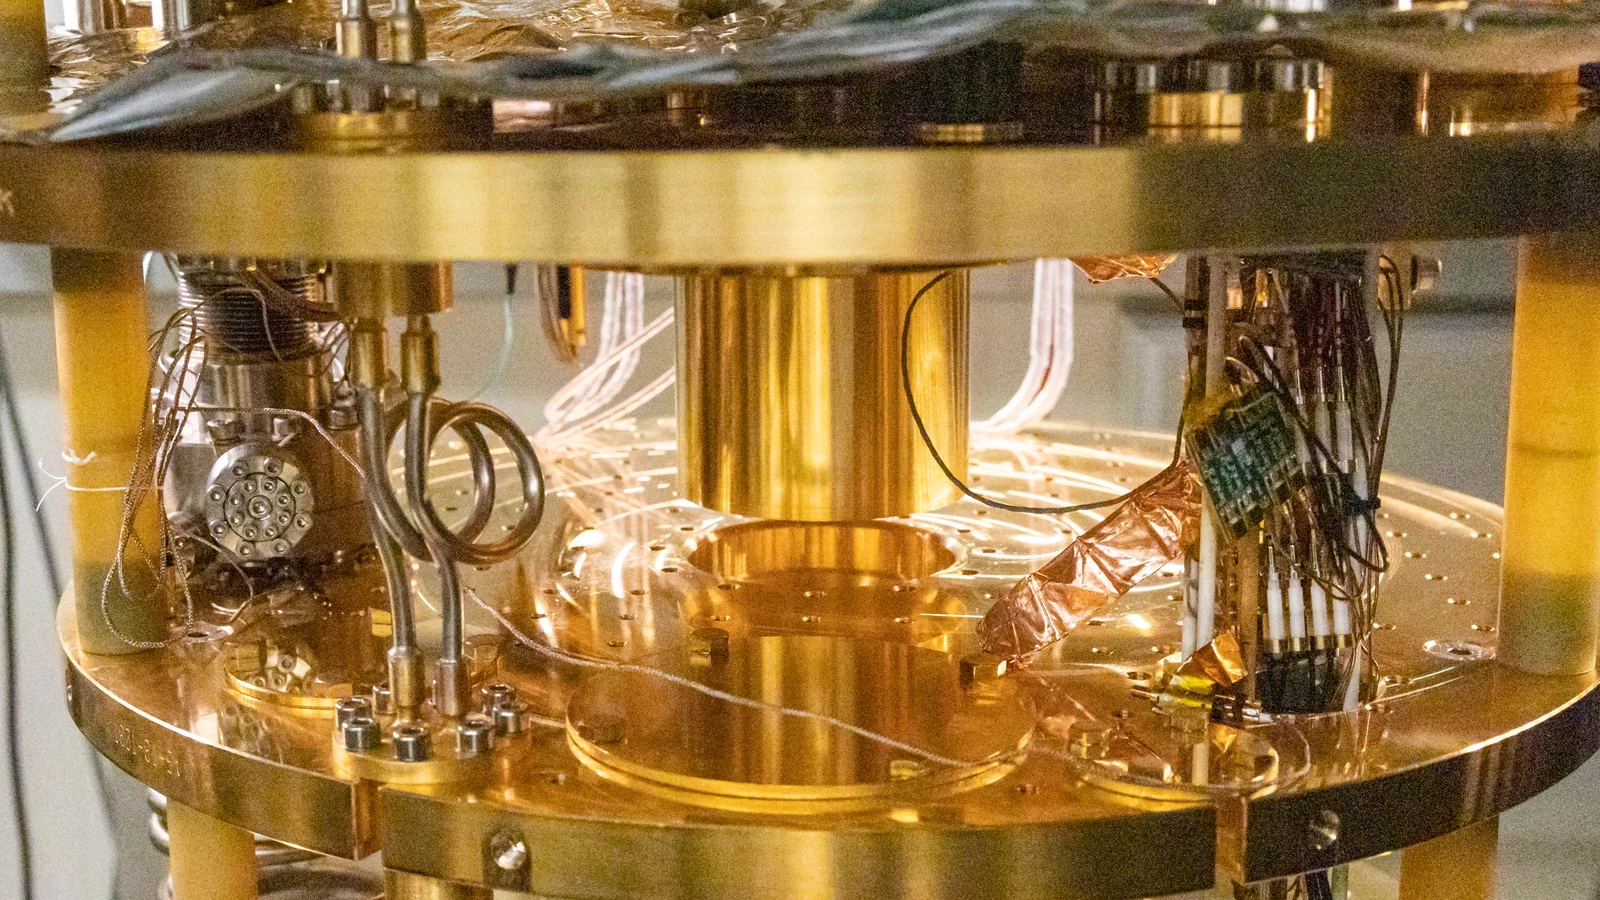
Photo by Oak Ridge National Laboratory, cropped from the original, licensed under CC BY 2.0.
The board question is no longer when quantum computers arrive. It is whether systems bought today can meet the security standards expected before their contracts and service lives end.
Quantum risk has often been treated as a question of scientific timing. That framing is now obsolete. On June 22, 2026, the United States issued Executive Order 14412, requiring federal high-value assets and high-impact systems to use post-quantum cryptography for key establishment by December 31, 2030, and for digital signatures by December 31, 2031. A related Office of Management and Budget memorandum requires agency migration plans within 120 days and calls for the broad federal migration to mitigate as much quantum risk as feasible by the end of 2030.
The dates apply directly to federal systems, but their commercial importance is wider. Federal technology is built through cloud contracts, software licences, managed services, hardware refreshes, identity systems, and long supplier chains. The order therefore turns a future cryptographic threat into a current qualification question for vendors and a current oversight question for their boards.
The issue is not whether a cryptographically relevant quantum computer exists today. OMB states that none is known to exist, while warning that progress may produce one in the coming decade. The issue is whether systems bought in 2026, particularly systems with long service lives, will still be capable of meeting the security standards expected in 2030 and beyond.
Shifting to quantum-resistant security takes years. This is a proactive, risk-informed decision to help customers stay ahead of potential future threats.
Mark Russinovich
Chief Technology Officer, Microsoft Azure
Visible adoption can create misleading confidence. An August 2026 measurement study of 4,665 UK organisations found post-quantum key exchange support on 44.0% of reachable HTTPS services but only 6.4% of reachable SMTP services. Among organisations reachable through both protocols, only 144 supported the tested post-quantum mechanisms across both web and email infrastructure. Researchers found no post-quantum leaf-certificate signatures at all.
The gap matters because an organisation can appear ready at its website while its email, authentication, signing, embedded devices, internal services, or supplier integrations remain dependent on classical cryptography. The same study found that infrastructure provider identity was far more predictive of visible deployment than sector. One provider accounted for 69.7% of post-quantum HTTPS endpoints, while another accounted for 98.4% of post-quantum SMTP endpoints.
That concentration changes the governance question. A green indicator on an external scan may reflect a provider's default configuration, not a deliberate enterprise migration. Directors need evidence of organisational readiness, not evidence that one layer of the technology stack has moved first.
OMB's implementation memorandum is unusually explicit about vendor and third-party software. Agencies are told to include post-quantum integration in requirements for affected product categories and to define migration responsibilities with authorised cloud providers. It also instructs agencies to integrate upgrades into cloud migrations, software development lifecycles, and hardware refresh schedules.
That language establishes a practical template for commercial buyers. Procurement terms can ask whether a product supports NIST-standard algorithms, whether its cryptographic components are discoverable, whether algorithm choices are configurable, and whether the supplier has a tested migration path. Renewal rights, support periods, data export, key management, and end-of-life commitments now affect cryptographic resilience.
The board should not adjudicate algorithm design. It should test whether management can locate the contractual points where the company has transferred operational control without transferring accountability. A supplier that promises eventual compliance but cannot identify dependent products, certificate authorities, hardware security modules, or protocol constraints is offering aspiration rather than a migration plan.
Post-quantum migration is not a software patch applied on a convenient weekend. The United Kingdom's National Cyber Security Centre describes it as a mass technology change and estimates that large organisations may need two to three years for discovery, assessment, strategy, and an initial plan. Its roadmap targets completion of discovery and planning by 2028, early high-priority migration by 2031, and full migration by 2035.
Those horizons collide with ordinary investment cycles. Industrial control systems, payment infrastructure, connected products, medical devices, identity platforms, and long-lived network equipment can remain in service for years. Some use proprietary protocols. Some cannot accept larger keys or signatures without performance consequences. Some depend on suppliers whose own roadmaps are uncertain.
The capital implication is straightforward. If a system cannot support post-quantum or hybrid cryptography, the organisation may need to re-platform it, replace it, retire it, or accept a defined period of exposure. Each option has a different cash profile and operational risk. Boards reviewing technology capital plans should therefore distinguish routine modernisation from remediation made necessary by cryptographic inflexibility.
The most consequential quantum exposure may precede the quantum computer itself. Executive Order 14412 specifically cites the risk that adversaries collect encrypted information now and decrypt it later. OMB tells agencies to prioritise systems containing data expected to remain mission-sensitive in 2030.
For companies, that logic extends beyond classified information. Product designs, clinical data, long-term customer records, strategic transaction material, industrial process data, private keys, and certain legal archives can retain value longer than the encryption protecting them. A migration programme ranked only by system criticality can therefore miss the assets with the longest confidentiality life.
This is why cryptographic inventory must connect to information governance. Management needs to know not only where RSA, elliptic-curve cryptography, certificates, and signing keys are used, but also what those controls protect and for how long the underlying information must remain confidential or authentic. The risk clock begins with data capture, not with a future announcement from a quantum laboratory.
NIST standardised three core post-quantum algorithms in 2024: ML-KEM for key establishment, ML-DSA for digital signatures, and SLH-DSA as a hash-based signature alternative. The June 2026 federal memorandum gives those standards an operating timetable. It also requires support for TLS 1.3 no later than January 2, 2030, because the protocol provides a practical foundation for hybrid key exchange.
Standards, however, do not remove implementation tradeoffs. NIST FIPS 204 specifies ML-DSA signatures of 2,420 to 4,627 bytes, depending on the parameter set, while SLH-DSA signatures can reach tens of kilobytes. Hybrid architectures can preserve interoperability and defence in depth, but OMB describes them as intricate and resource-intensive. Performance, bandwidth, certificate chains, secure boot, device constraints, and rollback planning all require testing.
The strategic capability is therefore cryptographic agility. Systems should be able to change algorithms without a complete rebuild. That principle affects application architecture, key management, hardware security modules, protocol negotiation, supplier requirements, and configuration control. For directors, agility is the best defence against false precision about the exact arrival date of a quantum threat.
The first useful board artifact is not a quantum computing presentation. It is a risk-ranked cryptographic inventory tied to data lifetime, system ownership, supplier dependency, and replacement timing. The second is a migration portfolio that separates provider-enabled changes from work the organisation must fund and execute itself. The third is a procurement standard that prevents new cryptographic debt from entering through contracts signed today.
Oversight also requires a clear owner. The federal order defines a migration lead who reports to the chief information officer and is responsible for inventory management, prioritised planning, and coordination. In a company, the equivalent mandate will usually cross the CIO, CISO, chief risk officer, procurement leader, general counsel, and business owners. Fragmented ownership is itself a warning because the migration spans systems, data, vendors, and capital.
Board reporting should show coverage and exceptions, not a single readiness percentage. Relevant evidence includes the share of the cryptographic estate discovered, the proportion of long-lived sensitive data mapped to controls, the number of critical suppliers with dated roadmaps, the systems unable to support hybrid operation, and the replacement capital already included in plans. These measures expose the distance between an external security signal and a governable transition.
The 2030 date is a federal deadline, but procurement standards rarely remain contained within the original buyer. Cloud providers, software companies, defence contractors, financial institutions, healthcare suppliers, and critical infrastructure operators serve customers with overlapping security demands. Once product roadmaps, contract clauses, and assurance processes change for a major customer, the same capabilities can become a baseline elsewhere.
This does not mean every enterprise should copy the federal timetable without analysis. It means boards should treat 2030 as a credible external constraint when evaluating products, data, and capital with longer lives. Waiting for certainty about quantum hardware would ignore the slower and more controllable part of the problem: replacing embedded cryptography across a complex organisation.
The strategic question is no longer when quantum computing will break today's encryption. It is whether the company is still buying systems that will be difficult to secure when the standards, customers, or regulators require the change. That question belongs in procurement and capital planning now.
Ventrix Research Team • Sep 23, 2026
A board search can begin before the company agrees on the job. A clear recruitment brief defines the contribution, evidence and terms candidates need to assess.
Ventrix Research Team • Sep 21, 2026
Write a board bio for your first corporate board seat. Show relevant experience, substantiate your claims, and tailor your profile to a board mandate.
Ventrix Editorial Team • Sep 18, 2026
Oracle's September wind deals raise a board oversight question: how much capital is committed before a facility has the power it needs?